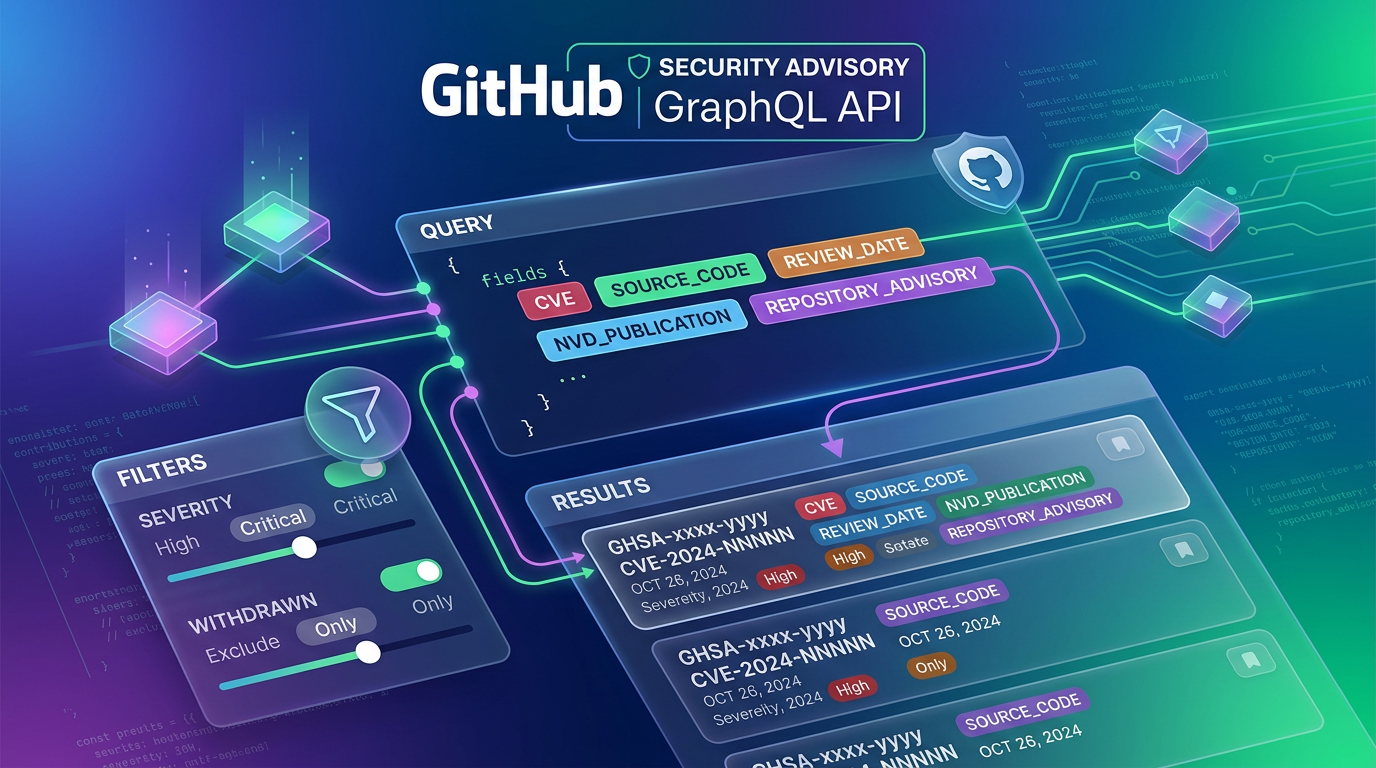
GitHub expanded the SecurityAdvisory GraphQL API on October 2, 2026 with additional metadata and server-side filters. The update makes vulnerability-management integrations more efficient by allowing developers to retrieve important advisory information through one GraphQL path instead of combining multiple API calls.
New fields
The SecurityAdvisory object now exposes the CVE identifier, affected source-code location, the time GitHub reviewed an advisory, the NVD publication time, and the URL of a linked repository security advisory.
New filters
The securityAdvisories query also gains severity and withdrawn filters. These filters can reduce the amount of data an integration downloads when it only needs high-severity issues or needs to audit withdrawn advisories.
Why this matters for security automation
Security platforms often combine GitHub advisories with vulnerability scanners, SBOM systems, ticketing tools, and risk dashboards. Every extra API round trip increases complexity and can consume rate-limit budget. More complete GraphQL responses allow these integrations to make richer decisions from a single query.
Practical use cases
A security dashboard can track when GitHub reviewed an advisory compared with when the NVD published it. A triage system can filter by severity before fetching details. Engineering tools can use the source-code location to connect an advisory to the relevant repository or component.
Practical takeaway
If you maintain a GitHub security integration, review whether your current REST and GraphQL calls can be consolidated. The new fields and filters can reduce round trips while preserving existing query compatibility.