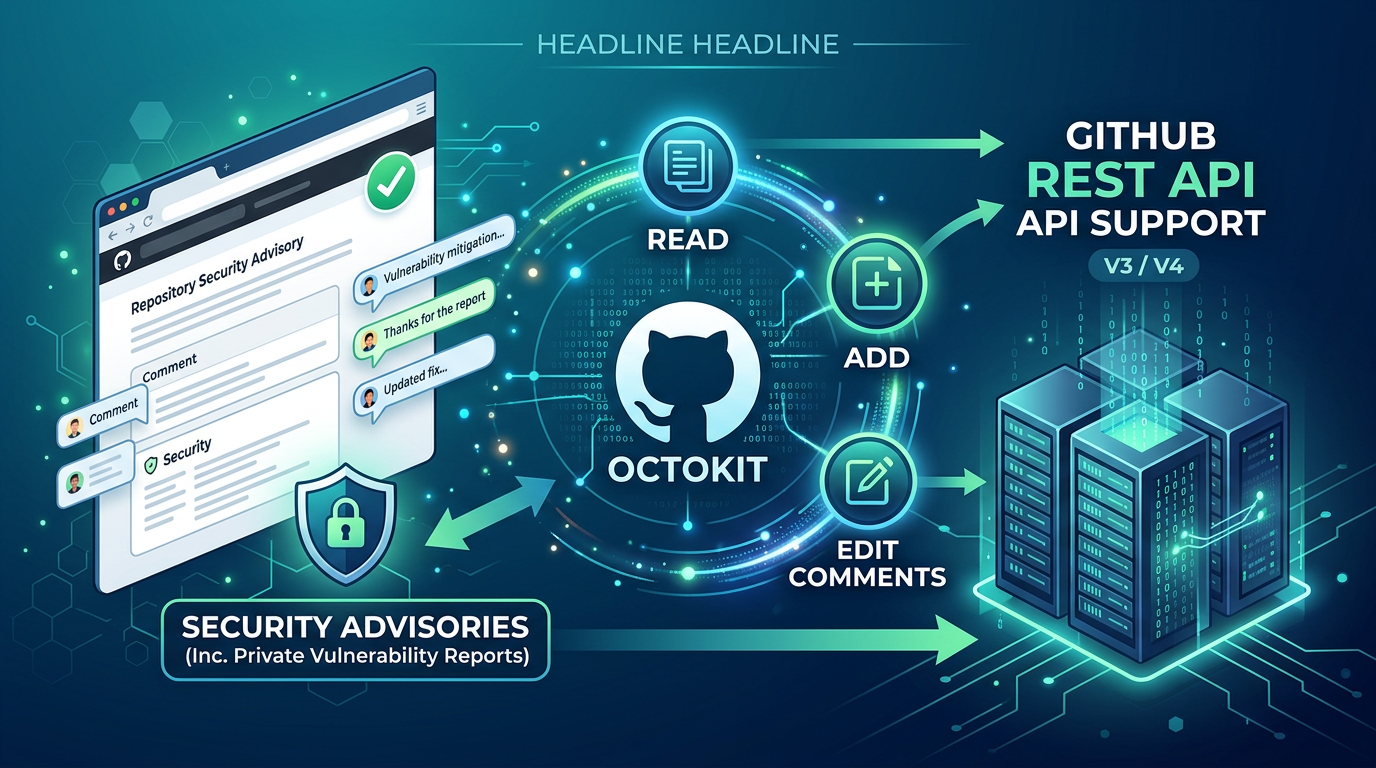
GitHub introduced a public-preview API for repository security advisory comments on October 2, 2026. Developers can now read, add, and edit advisory comments through REST endpoints, making vulnerability-triage discussions accessible to automated security workflows.
What the API adds
The new endpoints can list comments, retrieve an individual comment, add a comment, and edit an existing comment. Advisory responses also expose a comment count, helping automation identify advisories with discussion before fetching the full thread.
Why security comments matter
Security advisories often contain the operational context that turns a vulnerability record into an actionable incident. Triage notes can explain reproduction steps, affected versions, remediation decisions, and coordination between maintainers.
Automation opportunities
Security teams can use the API to export discussions for audits, synchronize triage information into internal systems, or automatically add notes when scanners and incident-management systems produce new evidence. The API also supports workflows around private vulnerability reports, subject to GitHub permissions.
Access controls
Access follows the permissions of the advisory itself. Confidential comments are not returned by these REST endpoints, so teams should not assume that an API export represents every conversation associated with an advisory.
Practical takeaway
Security engineering teams can now treat advisory discussions as another programmable part of the vulnerability-management workflow. Build permission checks and audit logging into integrations, and keep confidential discussion paths separate from ordinary advisory exports.
Source: GitHub Changelog — Repository security advisory comments API